

The Ultimate Guide to DevSecOps
A curated Irish edition of IndustrialDay news, analysis, interviews, reviews, job moves, and related resources for DevSecOps.
What to know about DevSecOps
DevSecOps represents the integration of security practices within the DevOps process, aiming to build security into every phase of software development and delivery. This approach helps organisations accelerate development cycles while maintaining strong security and compliance standards.
Exploring recent stories tagged with DevSecOps reveals a dynamic field where AI-driven tools, cloud-native security, and collaboration between development, security, and operations teams are shaping the future of secure software delivery. Topics such as risk management, container and API security, supply chain protection, and the rising importance of observability and automation are frequently discussed.
For readers interested in how organisations are addressing evolving cybersecurity threats while enhancing agility and innovation, the DevSecOps tag offers insights into technology advancements, cultural shifts, and best practices that help teams deliver resilient, secure software faster. Whether you are a developer, security professional, or IT leader, following DevSecOps stories provides valuable perspectives on securing modern software development in an increasingly complex digital landscape.
Analyst Insights
Research and market analysis connected to DevSecOps
Netskope launches control to block risky AI agent actions
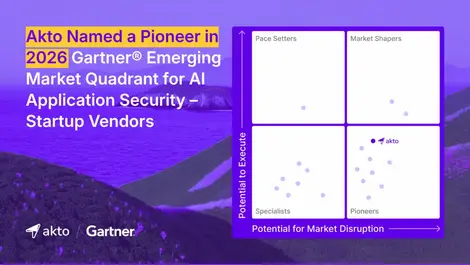
Akto named pioneer in Gartner's AI security quadrant
Coder launches Agent Relay for Cursor in private preview
RevEng.AI launches binary analysis models for code
Broadcom launches TrueSource for secure open source
Expert Columns
Supercharged security: Cyber risk in the age of frontier AI
AI deserves our appreciation, but only if we're honest about what we're appreciating
A strategic blueprint for governing AI-enabled software development
Your annual penetration testing is already out of date
As agentic development accelerates, workflow auditability becomes a bottleneck
Secure by default: Moving beyond secure by design
Why the next endpoint and SASE disruption will not come from a security vendor
The security challenges in AI-assisted software development
Interviews
Interviews and video coverage from the network
Recent DevSecOps News
StackHawk launches Wingman to fix flaws in AI coding
Security teams may cut backlogs as Wingman finds, fixes and verifies flaws inside AI coding tools before pull requests are opened.
Azul launches AI assistant for Java security checks
IT teams can now spot unpatched Java versions and Oracle licensing exposure in live production data, cutting the risk of audit surprises.
Datadog launches tools to monitor & test user journeys
The new tools aim to help teams spot when customers fail to complete checkout, sign-in or onboarding, despite healthy system metrics.
Stacklet launches Cloud AI FinOps Benchmark for cloud costs
Cloud AI bills are drawing new scrutiny as Stacklet targets waste across AWS, Google Cloud and Azure with tested controls.
UiPath adds AI agents to automate enterprise testing
Enterprise quality teams could cut manual testing as UiPath adds AI agents to run, explore and maintain tests across applications.
Gravwell unveils five AI agents for security teams
Security teams can now use narrowly scoped agents to triage alerts, investigate cases and check systems without giving AI unrestricted access.
Palo Alto launches continuous AI defence for clients
Attackers are exploiting AI faster than many defences can respond, prompting a shift to continuous testing for hidden exposures.
Fastly launches AI firewall & runtime control tools
Machine-generated traffic is driving up costs and security risks as Fastly adds controls for AI systems now moving into production.
GitLab 19.4 adds agentic automation & cost controls
Administrators now have tighter oversight as GitLab 19.4 expands AI agent controls, model choice and usage visibility across teams.
AI security incidents expose new criminal tradeoffs
Criminals are increasingly using AI for ransomware and credential theft, while flaws in test models are exposing production systems and data.
Mandiant warns of AI agents fuelling new attack risks
Autonomous systems are now creating fresh avenues for code theft, remote execution and runaway cloud spending, Mandiant says.
Rubrik launches Code Guardian & expands Anthropic ties
The private previews aim to help security teams spot exploitable code chains and connect AI agents to Rubrik's governance tools more safely.
EU software makers face new cyber reporting deadlines
Companies selling software into the bloc now have 24 hours to flag exploited flaws, with fines reaching EUR €15 million for delays.
Google warns of AI-powered cyberattacks in live ops
Defenders now have minutes, not hours, as attackers use agentic AI to automate credential theft, scanning and extortion across live operations.
SentinelOne adds OpenAI GPT-5.6-Cyber to AI services
Security teams could cut manual triage as the new service ranks code and intrusion risks by real-world exploitability, not alert volume.
Google warns cyber attackers are moving to agentic AI
Attackers are compressing intrusions into hours, leaving defenders less time to spot and stop credential-harvesting campaigns.
Abnormal AI launches cloud security for rogue agents
The new product aims to spot and contain malicious AI-agent activity in clouds as firms brace for faster, harder-to-detect attacks.
Checkmarx joins Anthropic's Project Glasswing on defence
The collaboration could help security teams spot flaws before attackers exploit them, as exploitations increasingly happen on or before disclosure.
F5 integrates AI Guardrails into MuleSoft Agent Fabric
Businesses using AI agents can now inspect prompts and responses inline, as F5's guardrails plug into MuleSoft's Agent Fabric.
Cycode launches agentic code scanning & attack chaining
Security teams could see fewer false positives and faster fixes as Cycode's new system blends rule-based checks with AI to trace attack paths.